
Ask clearly
Where you rely on consent, use a freely given, specific, informed and unambiguous choice. Pre-ticked boxes do not provide valid consent.
Good email marketing starts with a clear relationship with your audience. Understand how data protection and marketing rules fit together, and use Email Blaster’s tools to support your process.
The UK GDPR governs personal data processing. PECR sets specific rules for electronic marketing. A lawful basis for processing personal information does not, by itself, remove a PECR consent requirement.
For individual subscribers, email marketing generally needs consent unless an applicable soft opt-in exception meets its conditions. Corporate subscribers are treated differently under PECR; personal information and objections still need appropriate handling.
Sole traders and some partnerships are individual subscribers for these purposes. A business-looking email address alone does not tell you which rules apply.
Where you rely on consent, use a freely given, specific, informed and unambiguous choice. Pre-ticked boxes do not provide valid consent.
The products-and-services soft opt-in has specific conditions, including similar offerings and an opt-out when details are collected and in each message. It is not a general permission to email any contact.
Identify your organisation and provide a straightforward way to stop further marketing. Respect objections and withdrawal of consent.
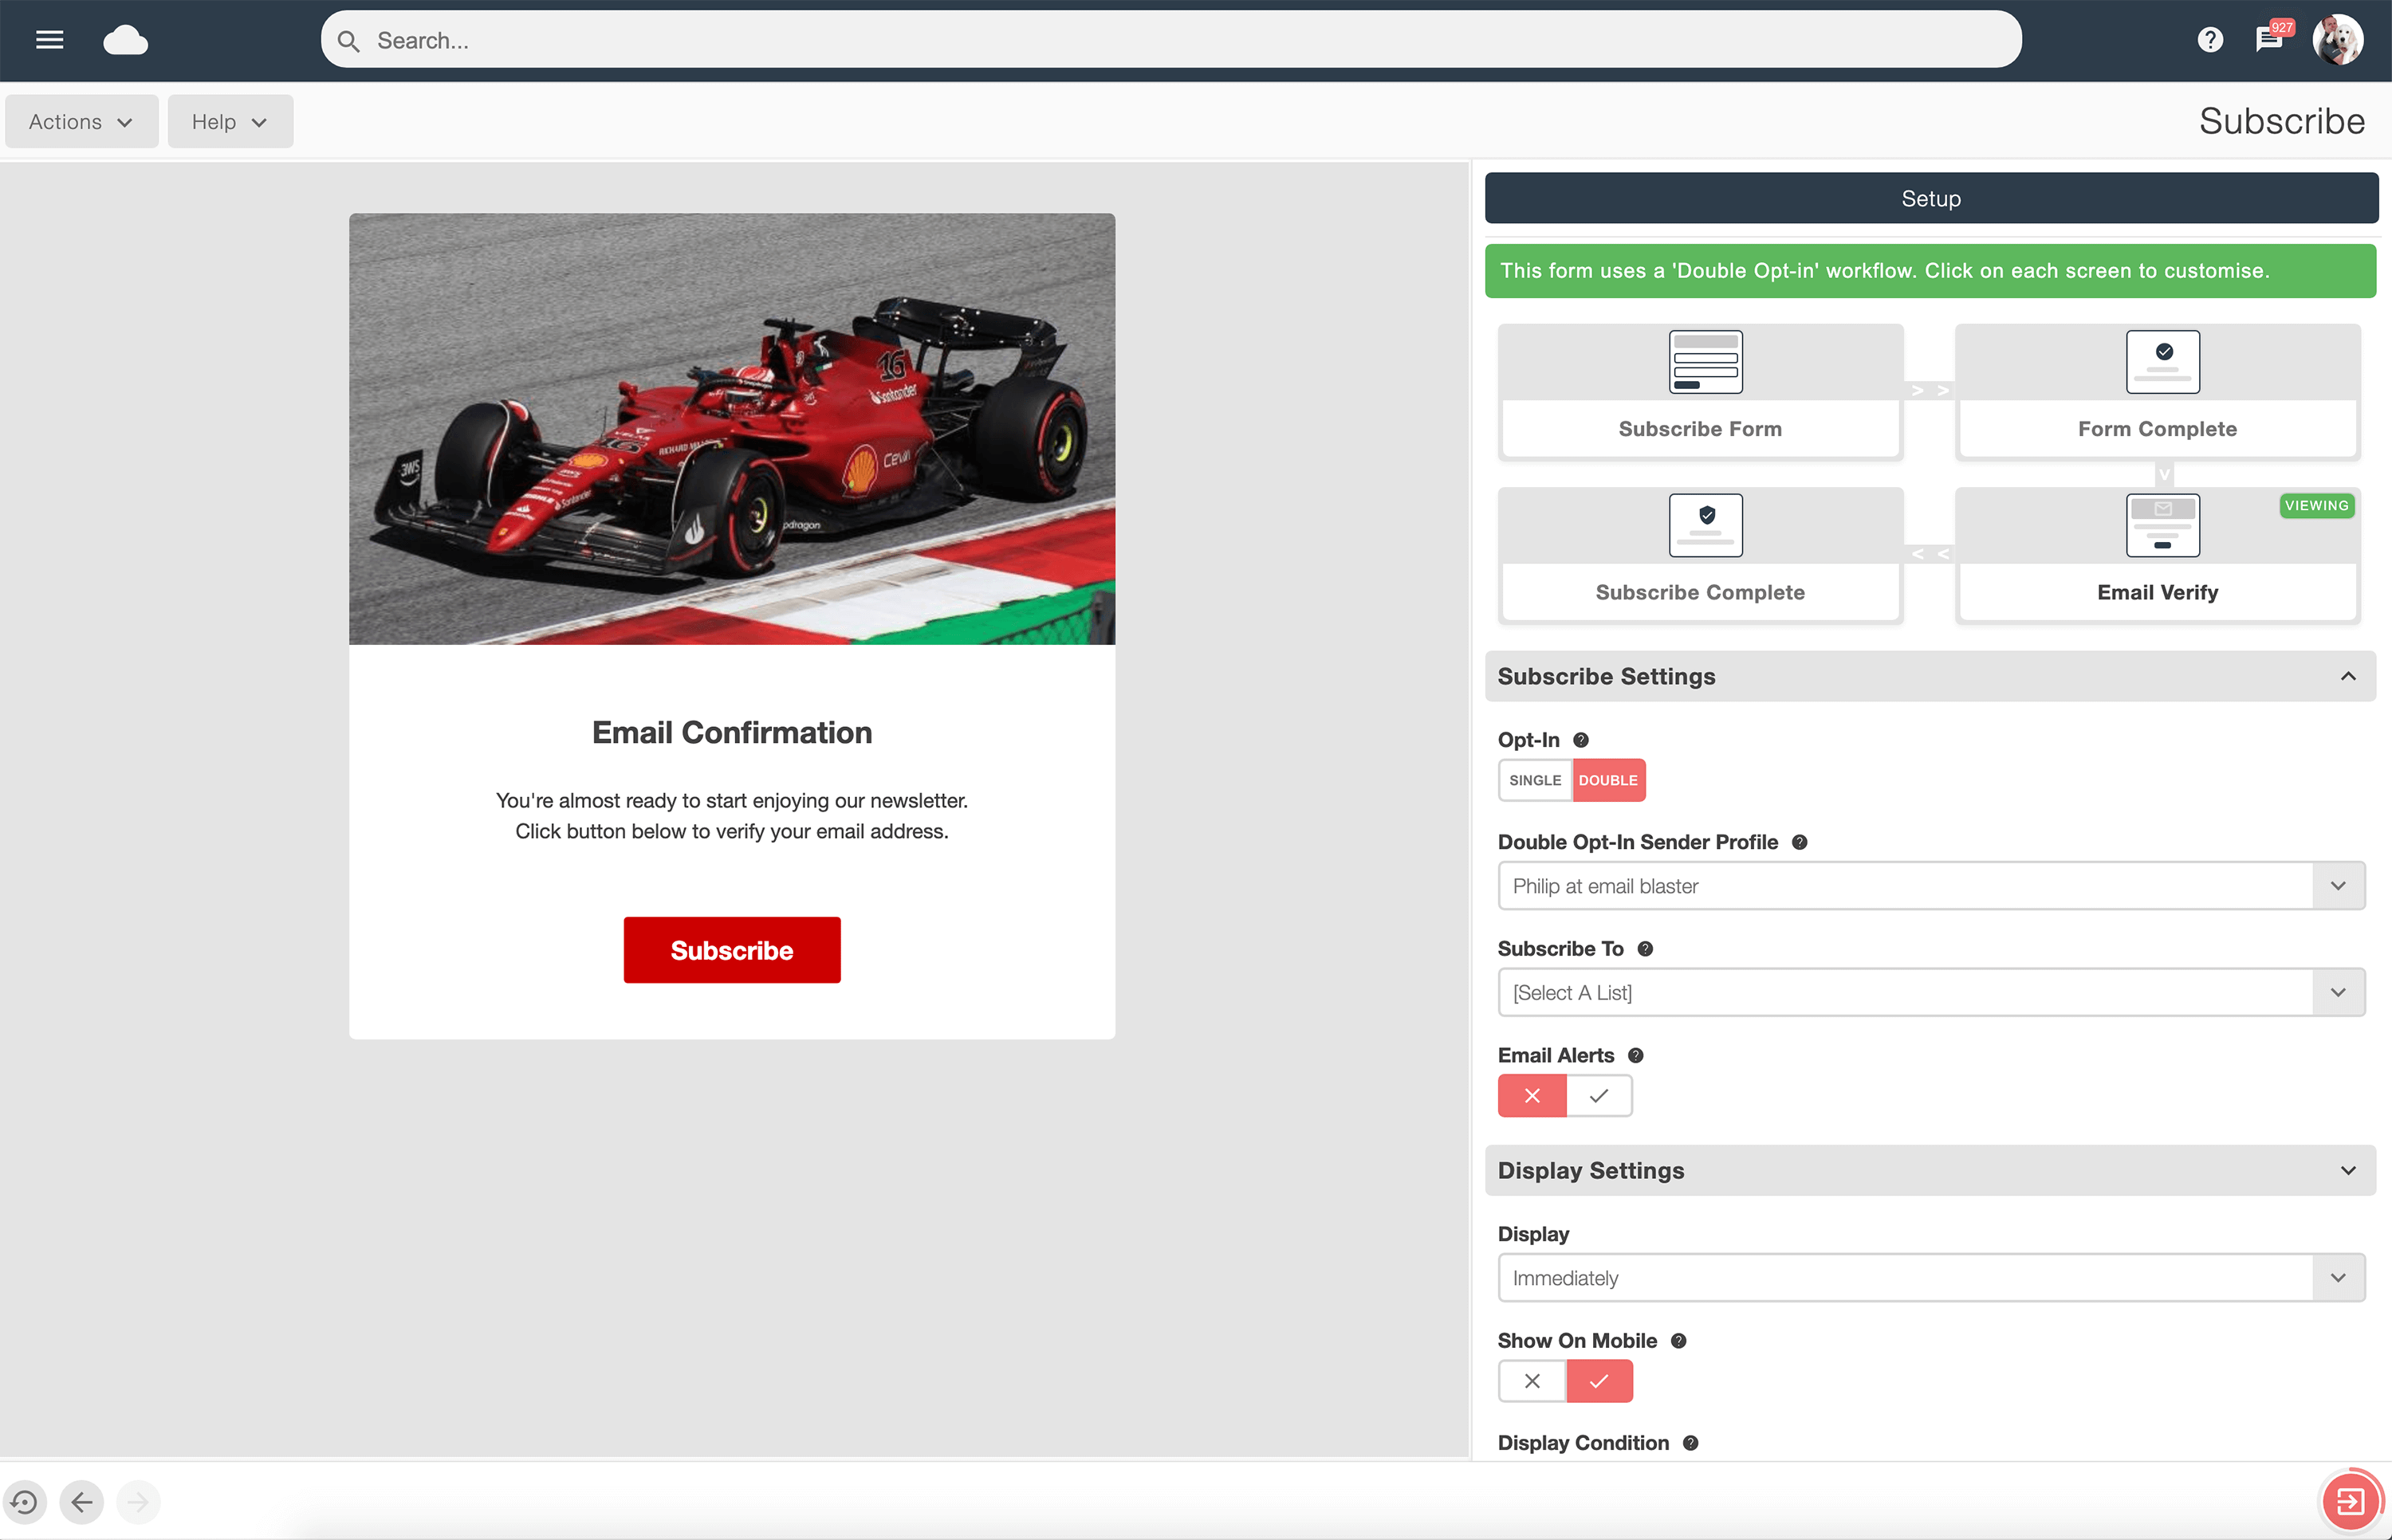
Use the subscribe form builder to explain what people are signing up for. Choose single or double opt-in and customise the confirmation experience to match your business.
Double opt-in helps verify an address and adds a confirmation step. It does not replace clear wording, appropriate records or responsibility for your use of the data.
Keep a record of the permission you rely on, including when and how it was obtained and what the person was told.
When someone objects to direct marketing, stop using their information for that purpose. Keeping the minimum necessary details on a suppression list can help prevent them being added back to future marketing.
An unsubscribe is not the same as a request to erase every record. Assess deletion requests and other rights separately, with appropriate records and retention decisions.
Use data cleansing alongside your permission records and preference-handling process.
Look for tools that support permission-based sign-ups, unsubscribe handling and responsible list management, alongside clear information about hosting and supplier responsibilities. Email Blaster brings these tools together with UK mailing-data storage and UK support. Your own processes and use of the platform remain essential to compliance.
Our sending policy requires positive opt-in for broadcast lists and prohibits purchased or third-party lists. The fact that a marketing activity may be permitted in a particular legal situation does not mean it meets the platform’s requirements.
Review our terms of service before importing or sending to a list, and ask our team if you are unsure whether your audience meets the policy.
For mailing-list processing, your organisation generally acts as controller: you decide why and how the data is used. The provider acts as processor when carrying out that processing on your instructions.
A controller-processor relationship needs appropriate written terms. Review the services, instructions and responsibilities, rather than assuming the software alone ensures compliance.
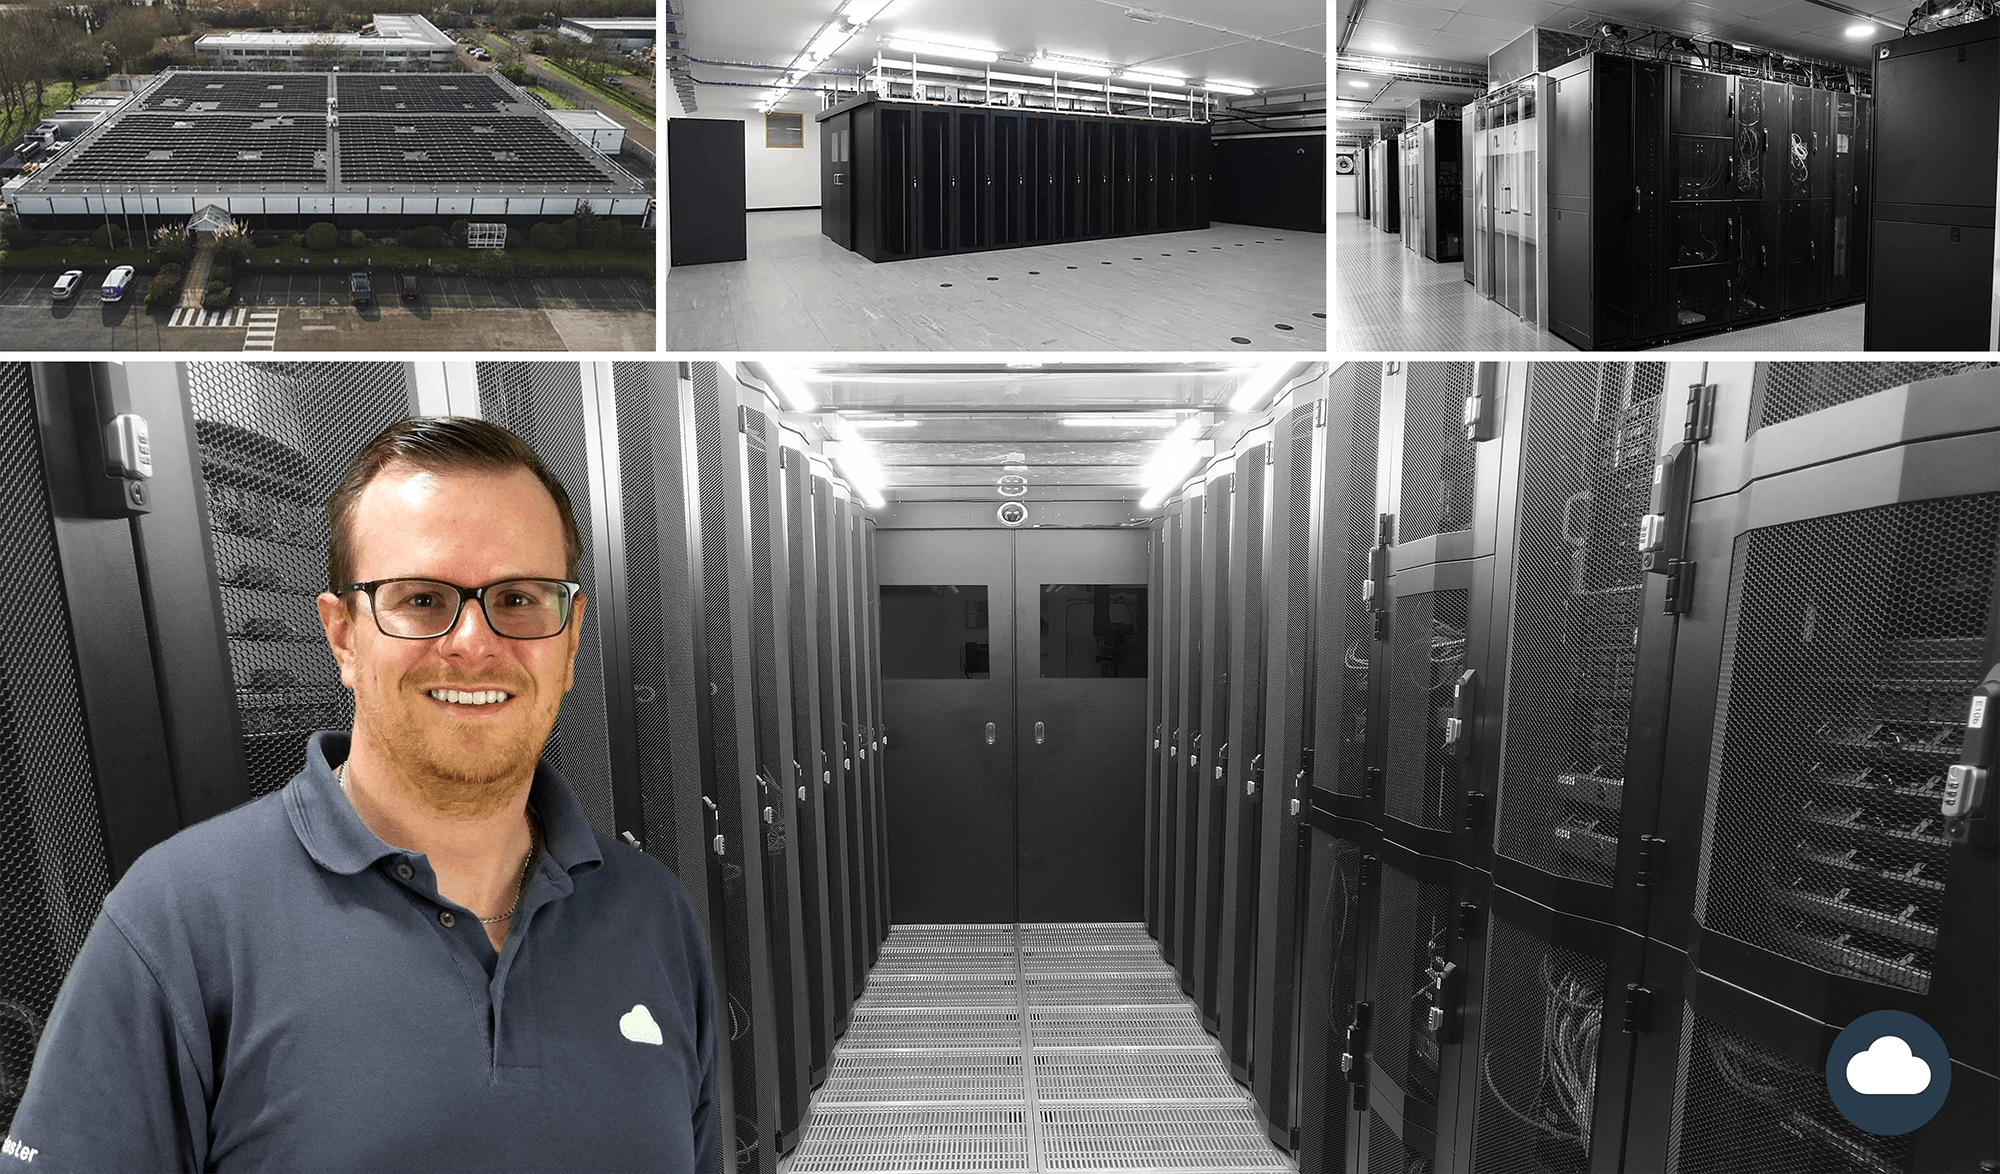
Email Blaster stores customer mailing data on UK infrastructure. Learn more about our UK-based network and team.
UK GDPR does not impose a blanket requirement to store all personal data in the UK. Transfers outside the UK may require safeguards; assess the relevant arrangements when reviewing any supplier.
Read the ICO’s international transfer guidance ↗.
This page is a practical overview. Use current ICO guidance and advice suited to your organisation when assessing specific obligations.
Explore our UK email marketing software or talk to the team about sign-up forms, mailing-list tools and your account setup.